When India’s Digital Personal Data Protection Act moved from draft to enforcement, the compliance bar shifted overnight—from interpreting the law to proving adherence, with live audit trails and documented evidence. For Himanshu Gautam, Founder & CEO of GoTrust, that shift confirmed an early bet: Indian enterprises would eventually need privacy infrastructure as rigorous as anything built for GDPR, but engineered for DPDP’s own logic. In this conversation, Gautam explains how GoTrust’s multi-agent AI system handles DPIAs and ROPAs without human bottlenecks, why the company chose on-premises deployment against the industry’s cloud-native tide, and what it takes to convince a CISO to trust an algorithm with judgment calls that once belonged to compliance officers alone.
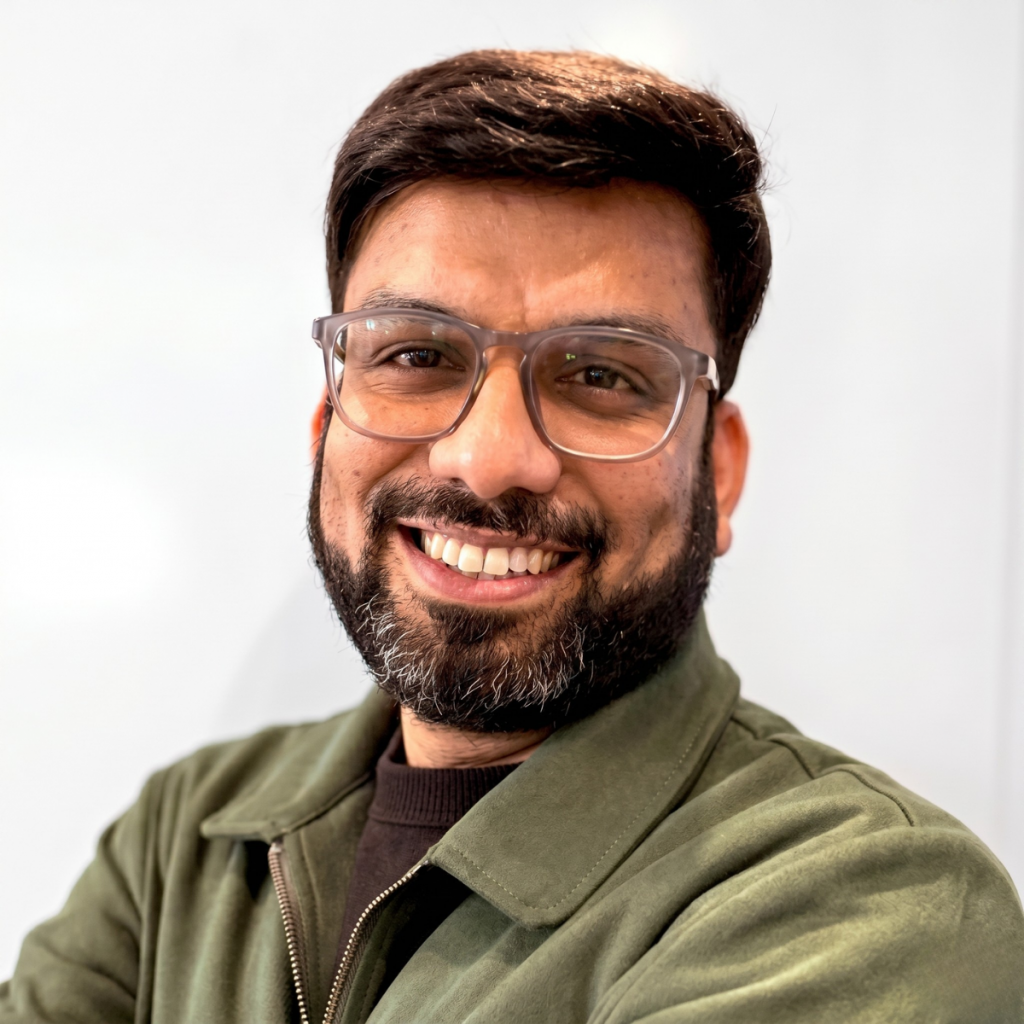
Founder & CEO
GoTrust
CISO Forum: What gap in the market pushed you to start GoTrust, and how has that thesis evolved as DPDP moved from draft to enforcement?
Himanshu Gautam: The gap was obvious to anyone who’d worked in Indian enterprises before DPDP existed: privacy was treated as a legal checkbox, not an operational system. Global platforms were built for GDPR-first markets and bolted on India as an afterthought. We started GoTrust betting that India’s privacy law would eventually demand the same operational rigour as GDPR, just with its own logic around consent, data fiduciaries, and localisation.
That thesis has held, but the problem changed once DPDP moved from draft to enforcement. Draft-stage compliance was about interpretation and preparedness. Enforcement-stage compliance is about proof, live audit trails, demonstrable consent records, documented DPIAs. So we had to shift the platform from “helping you understand DPDP” to “helping you prove DPDP,” which is a much higher bar.
CISO Forum: Walk us through how your multi-agent AI handles a DPIA or ROPA from start to finish, without human bottlenecks.
Himanshu Gautam: Break it into what a human compliance team actually does in sequence, and assign an agent to each stage instead of one person carrying the whole thing.
• A discovery agent maps what personal data is being processed, where it lives, and how it flows between systems
• A classification agent tags that data against regulatory categories, sensitive personal data, financial data, health data, and so on
• A risk-assessment agent runs the DPIA logic itself, scoring likelihood and impact against the specific processing activity
• A documentation agent drafts the ROPA or DPIA report in the required format, citing the data flows and risk scores the earlier agents produced
• A review agent checks the output against the applicable framework before it’s routed for sign-off
Each agent hands its output to the next, so the whole chain runs without someone manually rekeying information at every step. In other words, the human bottleneck we’re removing isn’t judgment; it’s the manual assembly work between judgment calls.
CISO Forum: Why on-premises, when most of the industry is racing toward cloud-native SaaS?
Himanshu Gautam: Because a meaningful share of the enterprises we serve legally can’t or won’t put certain data in someone else’s cloud. Banks, government bodies, and healthcare providers in India, the UAE, and parts of Europe operate under data localisation mandates or internal risk policies that rule out cloud-only compliance tooling for their most sensitive workloads. Cloud-native is the right answer for much of the market. It’s the wrong answer for the part of the market that needs sovereignty guarantees more than it needs convenience. We built on-premises as an option because ignoring that segment meant ignoring some of the highest-stakes compliance problems.
CISO Forum: How do you convince a CISO to trust an AI agent with tasks that used to require a compliance officer’s judgment?
Himanshu Gautam: You don’t ask for that trust upfront; you earn it by keeping the agent’s reasoning visible. Every automated decision, a risk score, a classification, a gap flagged, comes with the data and logic behind it, so a CISO can audit the agent’s judgment the same way they’d audit an analyst’s. We also don’t position the AI as replacing sign-off authority. It compresses the work that used to take a compliance officer days, and hands them a reviewed, defensible output to approve. Trust builds once they see the agent is consistent, transparent, and doesn’t quietly make judgment calls it should escalate.
CISO Forum: You’ve grown 500% year-on-year with 3–5-year enterprise contracts. What’s driving that retention, and what would break it?
Himanshu Gautam: Long contracts in this space aren’t won on a sales pitch; they’re won because switching compliance infrastructure mid-audit-cycle is genuinely painful for a client. Once GoTrust is embedded in how an enterprise runs its privacy program, ripping it out has real cost. That stickiness comes from clients starting with one module and growing into DSPM, TPRM, or AI governance as their needs mature, which compounds the growth.
What would break it is simple: losing the trust that our automated outputs are accurate and audit-ready. The moment a client’s regulator or auditor finds a gap in something our platform certified, that relationship is at risk regardless of contract length. Retention comes down to one thing: staying right.
CISO Forum: Honda, Nykaa, Bajaj Group, ICICI these operate in very different regulatory and data environments. How does GoTrust’s platform flex across that range without becoming generic?
Himanshu Gautam: Those four alone span automotive, e-commerce, financial conglomerate, and banking, each with different regulators, data types, and risk tolerance. The platform stays specific by separating what’s universal from what’s not—data discovery, classification, and workflow orchestration run on the same engine for everyone. What flexes on top is the regulatory logic layer, mapped separately to DPDP, sector-specific RBI or IRDAI guidance, GDPR, or UAE PDPL, plus risk thresholds configured per client based on their actual data sensitivity and exposure. So the core doesn’t get diluted trying to be generic, and the compliance layer doesn’t get forced into a one-size template.
CISO Forum: DPDP, GDPR, DSPM, DLP, GRC that’s a lot of acronyms under one roof. Is GoTrust building a platform or stitching together point solutions?
Himanshu Gautam: Platform, and the acronyms tell you either way. If DPDP, GDPR, DSPM, DLP, and GRC each lived in a separate tool, an enterprise would reconcile five different data maps and still do the integration work manually, which defeats the purpose. GoTrust runs on one underlying data map. DSPM and DLP both act on the same discovered and classified data set that ROPA and DPIA draw from, and GRC sits on top pulling evidence from all of it. If we were stitching point solutions together, that data model wouldn’t be shared, and every acronym would need its own audit trail.
CISO Forum: What’s the biggest blind spot you see in how Indian enterprises are approaching DPDP compliance right now?
Himanshu Gautam: Treating DPDP like a one-time documentation exercise instead of an operational shift. Many enterprises build consent banners and policy documents and call it done, without addressing whether their internal data flows, vendor contracts, and retention practices match what they’re now legally representing. DPDP enforcement will expose that gap between paper compliance and operational compliance, and the enterprises treating it as a checklist are the most exposed.
CISO Forum: As GoTrust expands into the UAE and Europe, how do you navigate the tension between India-specific DPDP logic and the more mature GDPR framework?
Himanshu Gautam: We don’t try to make one framework’s logic fit the other, because they genuinely differ; DPDP’s data fiduciary model isn’t a direct mirror of GDPR’s controller-processor structure. Instead, the platform treats each regulation as its own rule set operating on a shared data foundation. An enterprise operating in both India and the EU gets DPDP-specific and GDPR-specific assessments run against the same underlying data map, rather than a single blended assessment that misrepresents either law. The complexity is in maintaining that separation accurately as both frameworks evolve, not in forcing convergence where none exists.
CISO Forum: Where does AI-powered compliance automation break down, and what still needs a human in the loop?
Himanshu Gautam: It breaks down at ambiguity and consequence. AI is strong at pattern recognition across large data sets, flagging where sensitive data lives, spotting gaps against a known framework, and drafting standard documentation. It’s weaker where a regulation is genuinely open to interpretation, where enforcement precedent doesn’t exist yet, or where a judgment call carries real legal or reputational consequence for the business. DPIA risk scoring, incident severity classification in genuinely novel scenarios, and any decision that would need to hold up before a regulator still need a human compliance officer’s sign-off. The agent’s job is to do the work that makes that human decision faster and better-informed, not to make the decision itself.