Seclore’s Nilesh Bhojani says AI agents have changed the maths of data risk, making perimeter-era controls inadequate for enterprises.
AI agents have rewritten the maths of data risk. For years, enterprise data security rested on a simple assumption: humans accessed data for a purpose, and most documents stayed unopened. AI agents have broken that assumption. A single query from a mid-level employee can now send an agent through thousands of files in seconds, raising the risk of exposure even when access controls remain unchanged.
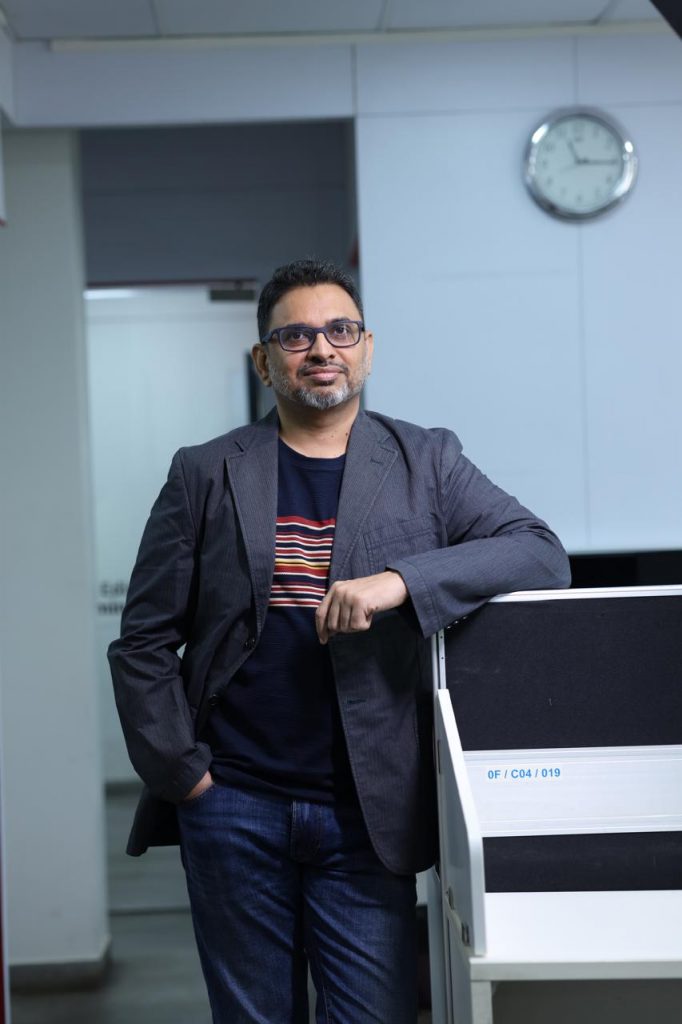
In this conversation with CISO Forum, Nilesh Bhojani, Chief Product and Technology Officer at Seclore, explains why perimeter-focused tools, regex-based DLP and standalone discovery scans no longer keep pace. He outlines how Seclore’s ARMOR framework brings discovery, classification, protection and proof onto one platform, and how context-preserving masking keeps sensitive data away from frontier models. He also says chained agent actions, where each step looks legitimate, but the sequence is risky, remain largely unsolved across the industry.
For CISOs moving to production, his warning is blunt: old controls will not hold against AI agents.
CISO Forum: When AI agents can independently access, interpret, and act on enterprise data, what breaks in traditional security models built around human users and static policies?
Nilesh Bhojani: Traditional security has always assumed humans use data for a purpose. Most data security focuses on the perimeter, on where the data sits. When AI enters the system, those assumptions no longer hold.
Over the last two or three years, organizations have been surprised by AI usage already happening within them, whether approved or not. These AI agents, whether chatbots or agent-led AI, have access to thousands and millions of topics. The access controls have not changed. What has changed is the probability of exposure, because risk is always about probability and impact.
When a document contains sensitive data, if it gets leaked, there is a certain amount of impact. But if the probability of that data being leaked is extremely low, you are not really worried, since there is a one-in-a-million chance the document might be leaked. Employees in the organization had access to thousands of documents but never opened them.
So, you are not so worried. You had time to deploy your DLPs and configure manual policies and run scans and all. But with AI coming in, a mid-level employee might run one query, and that agent might go and run a thousand documents. Suddenly, the speed at which document data gets extracted has increased. The probability of that has gone up; the probability math changes.
And that is why your traditional security is no longer enough. AI changes the game by increasing exposure, speed, and probability. You cannot just use different tools for different checks and manual scans. You need to act without waiting for remediation.
CISO Forum: Seclore’s ARMOR framework brings together discovery, classification, enforcement, and proof. Why did these need to converge into a single system now, rather than remain separate tools stitched together?
Nilesh Bhojani: These tools each do their own work. Discovery tools scan the data and show where it lies. Posture management and posture visibility tools show what permissions exist. Classification tools provide sensitivity labels that indicate the category of data.
Protection is the ultimate holy grail: ARMOR allows persistent protection and granular access control. In the age of AI, each tool does its own job, so the real value is integration.
Someone needs to sit in between and say, “Okay, this is the data for X, and this is the data for Y,” but that is no longer acceptable at the speed at which AI is operating within organizations. That is why we believe the answer is a holistic platform: a single platform that gives security teams the power to take control of the data and apply protection with a single click.
Now, having a human in the loop is important at various points to build confidence and provide checkpoints. But once you have confidence in the tools, you can automate these workflows. Having that inside a single tool means you do not have to run around connecting three or four disjointed systems and wait months before you can take any action.
CISO Forum: DSPM has largely been about visibility, knowing where sensitive data lives. What specifically does ARMOR DSPM do beyond discovery, and how does it connect that visibility to actual risk reduction?
Nilesh Bhojani: Discovery tools have been around for nearly two decades, since around 2007-2008, when DLP started. Early Gen 1 DLPs and discovery tools checked data using regex and pattern matching, and they became slightly more sophisticated over the next decade.
Then came machine learning-based ML classifiers, or trainable classifiers; this is what we call Gen 2 discovery tools. Over the last three years or so, with the advent of Gen AI, we can understand not just the content of data but also the semantic triad of content, context, and intent.
And when you combine these three, what you really understand is what this data is, why it is there, and who is supposed to be using it. That is the discovery part. But where most DSPMs stop is by just telling you that this is the data and there is a risk.
But what most of them don’t do is give you the ability to take action to reduce that risk. With ARPA, our philosophy is to extend SIGGRAPH’s 15 years of protection heritage, where we have expertise in protecting data, not just in providing and distributing data, and to extend that by allowing customers to have an end-to-end workflow from discovery to classification to protection.
And that’s what ARPA brings to the table, which no other DSPM does today. Most of them would do some bits and pieces of it, but they don’t do it in the variety of ways or in the most effective way that ARPA can for them.
CISO Forum: With ARMOR AI-DLP, what does “securing the AI interaction layer” mean in practice? Are you protecting the prompt, the retrieved data, the model output, or all three?
Nilesh Bhojani: When we talk about AI security, customers worry about employees using frontier models and about the agent-to-AI applications they are building in-house. Everyone wants to use AI’s power, but the risk is higher because many employees handle sensitive data. When they are exposed to these tools, sensitive data leaves the organization. In many cases, it leaves the country. That creates a trade secret risk and a compliance risk.
Data sovereignty is a major issue for many of the organizations we work with. What we are trying to do is make it a more accessible platform for all users and enable AI peerlessly, while ensuring that sensitive data does not leak. So what we do is make sure that before the data goes to the models, it is masked. We identify and mask the sensitive data using a method we call context-preserving masking. That allows AI models to deliver high-quality results, even if they do not see the sensitive data itself.
The data goes to them, but the sensitive part is masked with smart masking. When the data comes back, the results are returned to the user, and they are smart. So the end user does not see any difference; they are just writing the same prompt or providing the same documents. But none of the sensitive data contained in the document or the prompt reaches the frontier models.
CISO Forum: As copilots and RAG applications pull from enterprise data stores, how do you prevent sensitive information from leaking into an AI response, even when the underlying access controls are technically correct?
Nilesh Bhojani: Access controls govern what a user can access, or who can open or touch this document. Typically, security controls focus on the perimeter: you have access to this application or folder, but most controls do not go to the data level.
Do I have access to this data? With Secure’s EDRM technology, we ensure that not just the folder or application is secured, but the data itself is. That is the key reason our customers trust us. EDRM is a framework that allows organizations to secure data when they don’t want it exposed to their AI agents and tools. That is one part.
The second part is the whole AI DLP layer, where access control is in place, but the data should still not be leaked. So making sure that the right data is passed and it does not go out of the organization’s control is the second thing that is really, really important. In general, beyond SIGLO, it is also very important for organizations to start from identity. Identity management is definitely an important part that works in conjunction with all the other security tools.
CISO Forum: Autonomous AI agents can chain multiple actions together. How does ARMOR handle a scenario in which each data access appears legitimate, but the cumulative sequence of actions poses a real risk?
Nilesh Bhojani: No tool is doing this today. It is a complex problem, not an easy one to solve. A three- or four-step action is not easy to solve, and three or four disjointed actions are being performed at a very rapid pace that agents can do. Understanding that is definitely a complex problem that we are currently investing in solving. We are also partnering with other enterprise security tools that are solving this problem. But as far as I understand from our own analysis and from talking to customers, it remains, to a great extent, an unsolved problem in which data is not accessed through a single endpoint.
There is a real challenge facing the industry today: we need to come together to solve these problems. We need not just security tools but also AI companies to partner with us to develop solutions to these kinds of challenges.
CISO Forum: What does the Seclore-Glean partnership change for a CISO’s day-to-day operations? What becomes possible that wasn’t before?
Nilesh Bhojani: With Glean, you know, the organizations get the power of knowledge- the existing knowledge that is there in the organization. Glean allows employees to access it quickly and in a meaningful way.
But it does not help security teams gain more control; in fact, it can create more problems at times. So, the Seclore plus Glean measure is that organizations will already have scanned their data and indexed their data for their Glean knowledge base.
Now, with Seclore Armor, you can analyze all your data without creating new connectors, deploying, or rescanning, and get a security view of it. And as a security team, you can get full control of the security posture that you have, and then be able to control what data should be exposed to specific employees or specific AI models.
CISO Forum: You’ve spoken about security needing to become a “system” rather than a collection of tools. What breaks down operationally when discovery, classification, and enforcement remain disconnected, especially in AI-driven environments?
Nilesh Bhojani: Discovery is standalone; it creates more tasks because it scans hundreds and millions of documents and identifies sensor data, PI, or a PCI line. For security teams, that means thousands of alerts and tasks added to an already long to-do list. With classification, you can apply labels so downstream systems can use them effectively. Combining discovery and classification is the first step to make sure visibility translates into action. But the classification label is just a tag. It only tells someone that a document is sensitive or confidential. While certain systems will respect that and take the necessary actions, if the document leaves the organization, the sensitive data has already been leaked. That is where the third step of protection comes in.
For highly sensitive data, you need a persistent protection layer. All three systems working together is the only way to have actual control. Otherwise, you are just creating a long list of to-dos, and understanding the risk does not mean you control it. As we pilot RAG applications that pull data from enterprise data stores, how do you prevent sensitive information from leaking into an AI response, even when the underlying access controls are technically correct?
So, as documents are discovered through the DSPM and labeled for classification, there are different ways organizations can approach this, and ARMOR helps them. One is that we ensure the organization understands not just the content of the data but also its context and intent so that the right teams can decide the security policies for the appropriate documents.
Then, with our classification tool, we make sure that the classification data is embedded in the document as well, so systems like Glean, Copilot, and others can read it and process the right data while the central data is not.
What is known as the approved AI and the shadow AI? Approved AI is meant to ensure that all your classified data is processed correctly. And the third part is your access control. So, access control in traditional systems is all about just the perimeter: when the data is inside a folder, then you have a certain access control. You move it to a different folder, then the access control automatically changes.
That is where EDRM is a powerful tool: even after the document has moved to a different folder or been shared with another user via email, FTP, or SFTP, your control persists.
Your control persists no matter where you send the document or how you share it. The access controls defined by the organization and the data owner are still enforced on the document. And that’s the only way you can have complete security.
CISO Forum: “Continuous proof” is one of ARMOR’s pillars. In an AI-native environment where access patterns change constantly, what does proof of compliance or control actually look like, and how do you sustain it over time?
Nilesh Bhojani: For a proof to be truly usable, it has to come from the system enforcing the control. Right from DSPM classification to the EDRM, being on a single platform means you have a single pane of visibility. You can make sure that what was discovered, what was classified, when it was classified, whether the classification changed over time, and that certain important documents were protected. Once they are protected, you can see the activities that happen in this document throughout the life cycle.
So even if you had a document on your desktop or mobile phone that was protected and then shared with someone, you can still see all the sections no matter where the document travels. All of this combined provides visibility for security teams and auditors, with a full trail from when the data was discovered to today regarding anything that has happened to it.
And that’s the only way you can make it as to anything that has happened with the data. That’s the only way you can make sure that whatever is required for compliance, whenever the questions come, whenever the auditors come knocking, you have the answers ready at the click of a button and not something that you would have to go and investigate case by case and take weeks and months.
CISO Forum: For CISOs moving from AI pilots to production, what’s the single most common blind spot: where they assume they have control over enterprise data but actually don’t?
Nilesh Bhojani: The control policy, or perception of control, has focused on implementing perimeter firewalls, DLP, and access controls. But at the speed things are changing, and at the speed users can access documents across different applications and data repositories,
That means that even though you had access controls that worked in the pre-AI era, those are no longer valid. If you are still assuming that your two-year-old access control or your three-year-old DLP regex definitions will protect you from the threats posed by AI systems, AI tools, and agents in your organization, you are making a big mistake.
The good news is that most security leaders are aware of this and have been working very actively. Whenever we talk to them, they constantly ask us to help them solve problems.
In fact, the origin of DSPM is from many of these requests from our own customers, the 400-plus enterprise customers that have been using SecLore’s classification and protection tools for more than a decade, to help them get visibility and control in a single tool. This helps ensure that they are not just letting AI roam freely in the wild, but can enable AI fearlessly.