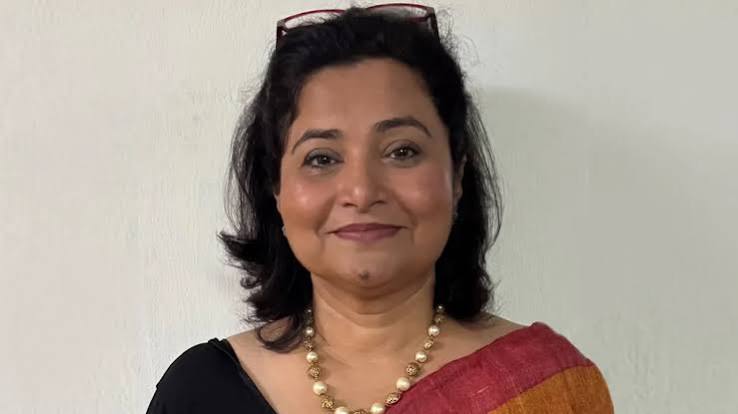
Sonia Ahluwalia of Kyndryl India says cloud success now hinges on accountability, with IaC, hybrid placement and governance managed as one system.
Enterprises have spent years moving to the cloud, yet many still struggle to prove the returns. According to Sonia Ahluwalia, Vice President – Cloud Practice, Kyndryl India, the problem is no longer adoption but accountability. In this conversation with the ET Edge CISO Forum, she argues that cost, governance, and performance must be managed as a single system, and that Infrastructure as Code is a board-level control mechanism, not a developer tool. She also explains why private cloud is returning as part of a deliberate hybrid strategy, how data residency rules under the DPDP Act and sector regulators shape workload placement, and what CIOs must get right before a hybrid overhaul.
CISO Forum: Enterprises have used the cloud for years, yet many still struggle to show returns. Where the gap between cloud adoption and value, and what is does a mature transformation look like today?
Sonia Ahluwalia: One theme that comes through consistently in discussions with enterprise leaders is that the challenge is no longer cloud adoption itself, but turning cloud investment into measurable business value. Many organisations moved quickly to cloud to address immediate technology or capacity needs, and are now asking a more fundamental question: how does the cloud estate contribute to growth, resilience, productivity and innovation? Kyndryl’s Cloud Readiness Report 2025 reinforces this pattern: 70% of CEOs believe their cloud environments evolved by accident rather than by design, even as organisations increased cloud spending by over 30% on average. The gap is not between the enterprise and the cloud; it is between cloud consumption and business accountability.
A mature transformation connects business outcomes, workload architecture and the operating model. It builds shared enterprise capabilities in governed cloud foundations, developer platforms, automation, observability, FinOps, and continuous modernisation.
CISO Forum: The conversation has moved from “cloud migration” to “cloud optimisation.” What are Indian enterprises getting wrong when they treat cost, governance and performance separately?
Sonia Ahluwalia: Cost, governance and performance are often handled as three separate management conversations, even though they are dimensions of the same operating decision. Finance may focus on spend, risk and compliance teams on controls, while engineering focuses on performance. If these decisions are made independently, savings in one area can create performance issues elsewhere, and controls can become inconsistent or expensive to operate. Over time, this creates governance and operational debt – complexity that can remain hidden until cost, risk and performance problems surface together.
The stronger model is to manage cost, performance, resilience, and risk as one system. That means bringing finance, engineering, architecture, security and business owners into a shared operating model with common telemetry and decision rights. FinOps then extends beyond bill reduction to include unit economics, accountability, forecasting, and continuous optimisation across public cloud, private cloud, and traditional environments.
CISO Forum: Infrastructure as Code is often seen as a developer tool. Why should a CIO or board care about it?
Sonia Ahluwalia: I would encourage CIOs and boards to look at Infrastructure as Code not as a developer tool, but as a control mechanism for the enterprise technology estate. In large hybrid environments, one recurring concern I hear from technology leaders is how to maintain consistency as infrastructure changes at speed and scale. IaC makes configurations repeatable, traceable and auditable, giving leadership greater confidence in what has been deployed, how it is configured and whether it conforms to approved standards.
The business relevance is significant. IaC reduces dependence on manual processes, improves consistency, and enables the embedding of security and governance requirements directly into provisioning. For a CIO, that translates into faster delivery with stronger control; for a board, it contributes to operational resilience, risk reduction and auditability. As infrastructure increasingly supports AI and digital services, the ability to make controlled, policy-compliant changes at machine speed becomes strategically important.
CISO Forum: How does IaC change consistency and policy compliance across public, private and hybrid environments? Can you give an example?
Sonia Ahluwalia: Across enterprise discussions, the challenge is rarely a lack of policy; it is applying policy consistently across increasingly distributed environments. Infrastructure as Code, combined with policy-as-code, allows organisations to translate requirements for identity and access, security, compliance, data governance, networking and observability into repeatable controls. The principle I advocate is to standardise enterprise guardrails while preserving application teams’ freedom to choose architectures and services appropriate to each workload.
Consider a regulated financial institution operating across public and private cloud. Instead of each team interpreting infrastructure and security standards independently, it can use approved templates to provision environments with a common baseline for access, networking, logging, encryption and observability. Automated policy checks can identify deviations before or after deployment. Compliance therefore becomes continuous and evidence-based rather than something reconstructed periodically for an audit. This is especially valuable where data access, resilience and regulatory accountability are critical.
This is also how we see infrastructure automation evolving: from scripts that speed provisioning to secure-by-design operating patterns. By combining Infrastructure as Code and policy-as-code, organisations can take an automation-first approach while maintaining the controls needed to accelerate cloud adoption, improve consistency and optimise cloud spend.
CISO Forum: Automation at scale can also spread misconfigurations. How do you build guardrails, security and auditability into code-driven infrastructure?
Sonia Ahluwalia: One concern I frequently hear from technology and risk leaders is that automation can amplify both good practice and bad practice. If a configuration is wrong, automation can reproduce that error at enterprise scale. The answer is therefore not less automation, but better-controlled automation. Infrastructure as Code should sit within a system of guardrails: configurations validated against policy before deployment, clear approval boundaries for higher-risk changes, complete traceability of what changed and who initiated it, and continuous monitoring for drift. For business-critical workloads, staged deployment, rollback and tested recovery procedures are equally important.
Those controls cannot stop at deployment. They need to extend into day-to-day operations through unified observability and policy-driven automation. The same principle is becoming increasingly important as enterprises introduce AI agents: organisations need explicit controls over data access, permitted actions, model usage, auditability and rollback. Kyndryl’s Agentic AI Framework, combined with policy-as-code capabilities, is designed to keep agents within approved actions and business rules, while Kyndryl Bridge provides visibility across IT environments. The leadership objective is straightforward: increase the speed and scale of automation without surrendering control of security, compliance or business-critical processes.
CISO Forum: Private cloud was once written off as legacy. Why is it back as a strategic platform, especially for regulated, latency-sensitive and cost-intensive workloads?
Sonia Ahluwalia: I do not see renewed interest in private cloud as organisations moving backwards. It is part of a more deliberate hybrid strategy. The question increasingly being asked at a workload level is: where can this application or data set deliver the right combination of performance, latency, resilience, security, regulatory control and economics? Public cloud, private cloud and on-premises infrastructure each have a role. The strategic shift is from ‘cloud first’ to choosing the right platform for the right workload.
AI is accelerating this discussion. Kyndryl’s 2026 State of Modernisation Report identifies AI as the second-biggest driver of private-cloud expansion. As organisations move AI from experimentation to production, they need to consider where sensitive data resides, where inference needs to occur, what latency is acceptable, and whether workload demand is predictable enough to justify dedicated capacity. Modern private cloud can provide software-defined infrastructure and automation while retaining greater control over the environment and data.
This is why modern private cloud should be viewed as part of the broader hybrid cloud architecture rather than as an isolated legacy platform. Kyndryl’s expanded alliance with OEMs enhances solutions with Kyndryl’s consulting, modernisation, and managed services expertise to support secure, AI-ready private cloud environments, including infrastructure for AI inference.
CISO Forum: With the DPDP Act and sector-specific rules from RBI, SEBI and IRDAI, how are data residency and sovereignty shaping workload placement in Indian enterprises?
Sonia Ahluwalia: Data residency and sovereignty have moved from being primarily compliance considerations to becoming architecture and governance decisions. It is important, however, to distinguish India’s broader privacy framework from sector-specific data residency or localisation requirements. The DPDP framework governs the processing and protection of personal data, while regulated sectors may have additional requirements for specific data, workloads, and outsourcing arrangements. Enterprises therefore need to understand what data they hold, its regulatory classification, where it is stored and processed, who can access it, and the controls that apply to it. This is driving a pragmatic mix of in-country public cloud regions, private cloud and hybrid environments, with governance and compliance considered at the architecture stage rather than after deployment.
CISO Forum: Many companies are repatriating certain workloads from public cloud. Is this a correction or a new normal, and how should leaders decide where workloads run today?
Sonia Ahluwalia: I see workload repatriation as a rebalancing, not a reversal of cloud adoption. There is noticeably less focus on moving everything to a single destination and much more on workload economics and fit. Enterprises are becoming more deliberate about the trade-offs among performance, cost, data sovereignty, resilience and operational control. Kyndryl’s 2025 Cloud Readiness Report reflects this: 84% of cloud leaders intentionally use multiple clouds, while 41% report repatriating at least some data to on-premises environments. That points to cloud strategies becoming more selective and workload-led, rather than enterprises abandoning cloud.
The decision should be made on a workload-by-workload basis. Leaders need to consider data sensitivity and regulatory requirements, latency and performance, utilisation patterns, long-term total cost of ownership, resilience requirements, and dependencies on cloud-native services. Equally important is understanding the existing application architecture, technical debt and dependencies before moving anything. A workload that appears cheaper to repatriate may incur new infrastructure and operating costs; another may derive significant value from public cloud elasticity or managed services.
The capability enterprises ultimately need is the ability to make and revisit placement decisions as requirements change. Consistent governance, security, automation, and observability across environments make this possible without allowing hybrid complexity to undermine cost control, resilience, or performance. The principle is straightforward: the right workload on the right platform, based on business requirements and evidence rather than a predetermined destination.
That balance between enterprise-wide consistency and workload-level choice is, in my view, the foundation of a sustainable multi-cloud strategy. It allows organisations to scale with confidence while keeping architecture aligned to changing business priorities.
CISO Forum: Everyone wants to be “AI-ready.” What does that mean for cloud infrastructure, and how does a full-stack hybrid approach support AI workloads without runaway costs?
Sonia Ahluwalia: Being ‘AI-ready’ is not simply a question of acquiring GPUs or consuming AI services. It is an enterprise architecture and operating-model question. AI in production depends on reliable, accessible and well-governed data; modern applications and integration patterns; appropriate compute, storage and network capacity; security and governance; and an operating model that can support AI services continuously. Without those foundations, organisations can run successful pilots but struggle to industrialise AI across the enterprise.
A full-stack hybrid approach provides an important lever: the ability to place different AI workloads where they make the most sense. Public cloud can provide elastic capacity and rapid access to AI services. In contrast, private cloud or on-premises infrastructure may be appropriate where data control, latency, regulatory requirements or predictable utilisation are priorities. Data gravity also matters: moving large or sensitive enterprise data sets solely to reach a model can introduce costs, latency, and governance implications. The architecture should therefore follow the workload, the data and the required business outcome rather than a fixed rule about where training or inference must run.
Economics must be designed into that architecture from the beginning. AI introduces new cost profiles across compute and accelerators, storage, network and data movement, model consumption and inference. Organisations therefore need visibility into utilisation, dependencies, performance and spend so that capacity and placement decisions can be adjusted early. Kyndryl Bridge provides visibility across IT environments, while Hybrid Cloud Cost Observability, Hybrid Cloud Control Plane, and Full Stack Observability provide capabilities for cost insights, governance, and operational visibility. The objective is to scale AI while maintaining control over cost, performance, security and risk.
CISO Forum: If you were advising a CIO starting a hybrid cloud overhaul today, what are the first three decisions they should get right, and what is the most common mistake you see?
Sonia Ahluwalia: If I were advising a CIO starting today, the first decision would be to establish an evidence-based view of the existing technology estate – business-critical applications, dependencies, technical debt, data flows and resilience requirements. This sounds fundamental, but it remains a major gap. Kyndryl’s 2026 State of Modernisation Report found that only 9% of organisations have fully mapped their business-critical applications and dependencies. Without that visibility, even a well-funded modernisation programme can encounter unexpected integration risks, cost and disruption.
Second, define workload-placement principles before selecting destinations: what should determine whether a workload runs in the public cloud, the private cloud, or on-premises? Those principles should include data, regulation, performance, resilience, economics and service dependencies. Third, design the operating model alongside the architecture. Security, access, cost controls, automation, observability and platform engineering need to work consistently across the hybrid estate rather than being added later.
The most common mistake I see is treating modernisation as a migration programme with a finish line. Migration changes where a workload runs; it does not automatically fix fragmented governance, manual operations, technical debt or resilience. The real test begins after go-live: can the environment be operated efficiently, secured continuously, recovered reliably and evolved without creating another generation of complexity? Modernisation therefore needs to become part of the operating model – a continuous discipline rather than a one-time move.