Every chatbot prompt, OTP request and WhatsApp message is now a potential attack surface. Generative AI has made impersonation credible enough and cheap enough to run at scale. Infobip’s Fraud & Security Report 2026 recorded a 77% rise in harmful messages in a single year, with phishing volumes up 94%.
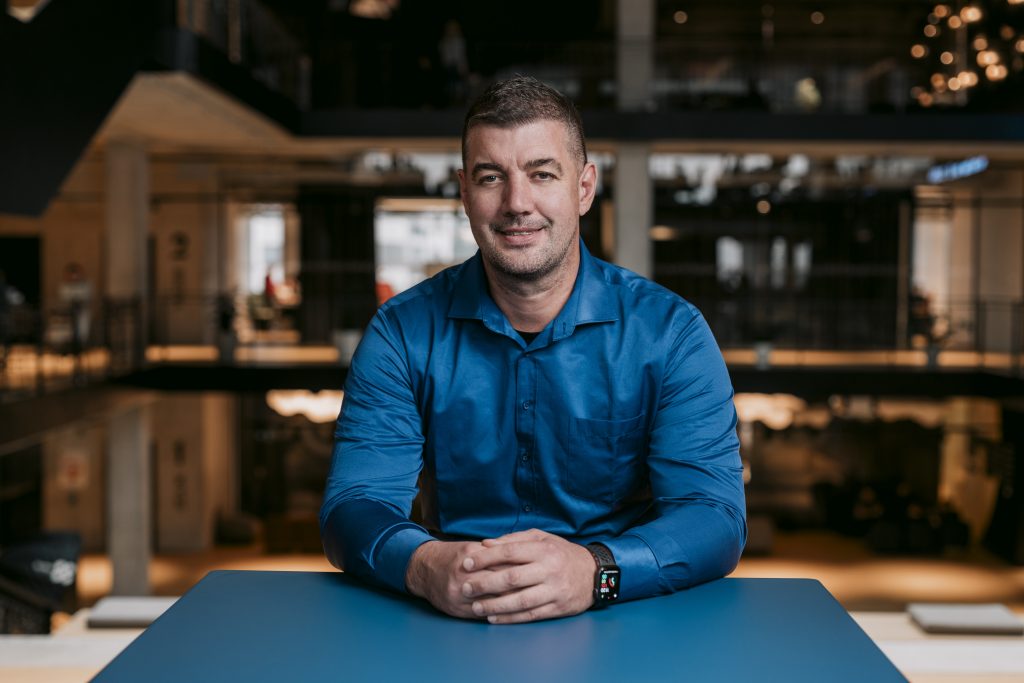
In this conversation, Matija Razem, Chief Commercial Telecom Officer at Infobip, argues that the security question has shifted from whether the platform is secure to whether customers can trust every interaction passing through it. He says personalisation and protection are a false trade-off. In these pinch points, CISO and business collaboration usually breaks down, and he explains why identity, communication and real-time network intelligence are converging into a single trust layer.
CISO Forum: Infobip sits at the intersection of customer communication and enterprise infrastructure. As AI becomes embedded in nearly every customer touchpoint, how has the security conversation around communications platforms changed in just the last couple of years?
Matija Razem: The security conversation has moved well beyond protecting the platform perimeter. Today, every interaction – whether it’s a chatbot prompt, an OTP request or a WhatsApp message – is a potential attack surface, and AI has made impersonation and phishing far more credible and cheaper to run at scale. Our Fraud & Security Report 2026 revealed a 77% increase in harmful messages in a single year, with phishing volumes up 94%. So the question is no longer, “Is the platform secure?” It is, “Can customers trust every interaction through it?” That is the shift: from securing infrastructure to securing trust at the point of conversation.
CISO Forum: Enterprises are under pressure to make customer engagement more intelligent and personalised, while also being told to lock down data and minimise risk. How do you see leaders reconciling these two mandates in practice? Is it a genuine trade-off, or a false one?
Matija Razem: I see this as a false trade-off. The best customer experiences are secure by design. Customers may not see the controls, but they notice immediately when a brand gets trust wrong. The practical answer is to use the right data for the right purpose: minimise exposure, apply clear consent and purpose limits, and let trusted signals such as Number Verification and SIM Swap detection reduce friction without extra customer steps. Enterprises are moving exactly this way – Network API interactions grew 91% last year. Customers do not want more friction; they want confidence that the interaction is genuine. Build security into the journey, and personalisation and protection reinforce each other.
CISO Forum: AI is increasingly used both to strengthen fraud detection and to power more convincing attacks: deepfake voice cloning, AI-generated phishing, and so on. From where you sit, is the balance of power currently tilted toward defenders or attackers, and why?
Matija Razem: Attackers currently have the speed advantage. Generative AI has lowered the cost of convincing phishing, cloned voices and targeted social engineering from weeks to minutes. Defenders, however, hold network intelligence, behavioural data and real-time signals that attackers do not control, and they are using them. Adoption of AI-powered fraud detection has grown 71% year-on-year, and pattern-based detection by 105%. So the balance is uneven, but not fixed. The issue is not whether AI favours attackers or defenders; it is whether enterprises deploy it as an integrated security capability, alongside verified channels, identity controls and human oversight, rather than as a standalone tool.
CISO Forum: What does a genuinely “secure by design” AI-powered communication ecosystem look like not just in terms of encryption and access controls, but in how the AI itself is trained, monitored, and governed?
Matija Razem: It starts with a simple principle: AI should access only the data, tools, and actions it genuinely needs. Encryption and role-based access are the foundation, not the finish line. Beyond that, enterprises need data discipline – knowing what enters a model, why and whether it can be used for training. Equally important is AI-specific testing for prompt injection, jailbreaks and hallucinations, with continuous monitoring once live. At Infobip, we believe that AI cannot be a feature bolted onto the communication stack; it must be governed as part of the enterprise risk architecture, with clear accountability for approving use cases and stopping a model that behaves unexpectedly. That is a continuous discipline, not a one-time compliance exercise.
CISO Forum: Identity-based attacks and social engineering are getting harder to spot as generative AI improves. What practical steps should enterprises be taking today to protect customers across channels like SMS, WhatsApp, voice, and email, where trust is often assumed by default?
Matija Razem: First, we need to stop assuming a familiar channel is trustworthy. Next, define how you will contact customers and what you will never ask for, and use verified sender identities so legitimate communication is visibly verifiable. Second, don’t depend on SMS OTPs alone for high-risk events. Network-based signals such as Number Verification and SIM Swap detection validate customers quietly, with less friction. At the same time, match controls to risk. A delivery update does not need the same safeguards as a password reset. Customer education is important, but it alone is no defence against deepfakes. Stronger, more structured safeguards are urgently needed.
CISO Forum: With data protection regulations tightening across markets, including India’s own privacy law, how should enterprises approach data governance for AI-driven customer engagement without slowing innovation?
Matija Razem: The right approach is to make data governance an innovation enabler rather than a compliance gate at the end of the process. Regulations such as India’s DPDP framework are pushing organisations toward clearer consent, accountability, individual rights, and breach preparedness. That should encourage better product design, not slower innovation.
In practice, build a reusable framework: classify data, map how it flows through AI systems, define permitted purposes and retention, and set a clear approval path for sensitive use cases. Enterprises should demand transparency from every technology partner on whether customer data leaves a geography or is used to train a model. Approved data sets and pre-vetted vendors then let teams innovate within guardrails.
CISO Forum: Personalisation depends on data, and data protection depends on restraint. Where do you draw that line, and how does it vary across industries, say, BFSI versus retail or healthcare?
Matija Razem: The line should be drawn at necessity, proportionality and customer expectation. Personalisation should improve a customer’s experience in a relevant, explainable way; it should not become an excuse to gather unlimited data or infer more than needed. In BFSI, the threshold is understandably much higher because the consequences of error, fraud or unauthorised disclosure can be significant – tighter consent, stronger identity verification, more conservative retention. It is no coincidence that the finance sector leads adoption of network-level verification such as SIM Swap and Number Verification.
Retail, by contrast, can operate with more flexibility when the value exchange is transparent and consent-led. Healthcare demands the strictest purpose limitation and human oversight. The common principle is that personalisation must earn trust. The more sensitive the context and the greater the potential impact on an individual, the more restrained, transparent and governed the use of data must be.
CISO Forum: You’ve spoken about CISOs and business leaders needing to collaborate more closely on customer-facing strategy. In your experience, where does that collaboration typically break down, and what does a healthy version of it look like?
Matija Razem: It breaks down because the two sides are measured differently: the business is rewarded for speed and conversion, and security for preventing incidents. So, security brought in at the final stage looks like an obstacle. In our experience, a healthy model brings the CISO, product, CX, legal and privacy teams together at the start, asking not “Can we deploy this AI capability?” but “What customer problem are we solving, what could go wrong, and how will we prove this interaction is trustworthy?” The most mature organisations we work with also define shared outcomes: lower fraud losses, fewer false positives, better authentication success. That makes security part of customer experience strategy, not a separate technical function.
CISO Forum: For enterprises deploying generative AI in customer interactions today, what’s one “responsible AI” practice you think is still underused or overlooked?
Matija Razem: Structured human oversight for high-impact moments. Many organisations talk about “human in the loop,” but few define it. A mature approach specifies exactly when AI can act autonomously, when it must seek approval, and when it hands over immediately, such as in the case of a disputed transaction, a vulnerable customer, or a suspected fraud event. Our view is that AI should be judged not on producing a fluent answer, but on knowing when not to answer, when to verify and when to escalate. That discipline improves safety and customer confidence, and it creates the human feedback loop that improves models over time, because people review the hardest edge cases rather than silently absorbing them into the system.
CISO Forum: Looking two to three years out, what’s the cybersecurity trend in enterprise communications that you think is currently underestimated, the one most leaders aren’t paying enough attention to yet?
Matija Razem: The most underestimated trend is the convergence of identity, communication and real-time network intelligence. For a long time, enterprises have treated messaging, authentication and fraud prevention as separate systems. Over the next two to three years, they will increasingly become one connected trust layer. As AI-generated impersonation grows, static identifiers such as a number, an email, or even a familiar voice will no longer prove identity. Early signals are clear: enterprise authentication is scaling beyond SMS-only security, and Infobip Signals helped enterprises cut artificially inflated traffic by 38%. Amidst this, organisations will instead need to validate context in real time – a recent SIM swap, a device or location that does not fit. Trust will no longer be assumed because a message arrives; it will have to be continuously proven.